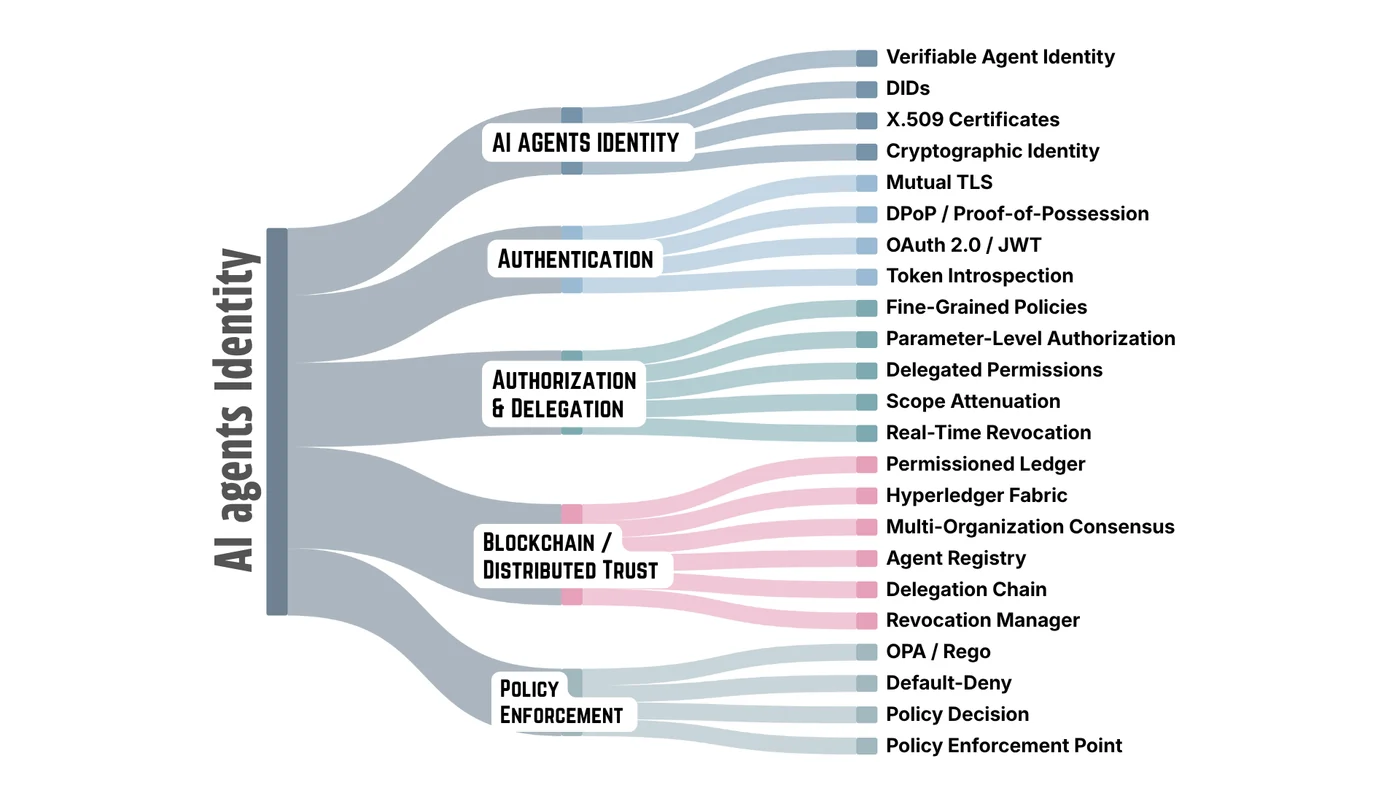
Open6GE extends AI agents beyond server operations into the telecom network stack, giving agents a verifiable identity and controlled authority to interact with RAN, Core, SMO, applications and infrastructure.
The approach uses cryptographic identity, proof-of-possession, policy-based authorization, delegated permissions and revocation so that every agent action can be authenticated and evaluated before it reaches a network function.
Authorization is evaluated down to individual parameters rather than whole interfaces, and revocation takes effect in real time, so authority granted to an agent can be withdrawn without waiting for a credential to expire.
Related
Related areas
Post-Quantum Security
Post-quantum cryptography across the telecom stack
Post-quantum and hybrid cryptography across the telecom architecture, with crypto agility as a first principle.
Read more →Automation from RAN to Cloud
Orchestration across RAN, core and cloud
Lifecycle and policy management across RAN, Core and cloud infrastructure through SMO, RIC and OTAF.
Read more →